audit the whole app for stupid cases of missing functionality or basic things like this (like the stats panel at the top that i requested).
"Like this" refers to his reports of the last hour: the webhook page did not show its retention period (#368 (comment)), the stats pane, the confusing target-add flow, the copy and add controls that do not look clickable, and the missing per-event view (#367 to #376).
PRIORITY: an owner's direct request, in the same tier as 367-376.
Definition of done:
One auditor who did not write the UI builds current next in Docker, runs it, and uses every page in headless Chrome the way an operator would. That covers sign-in, the webhook list, creating a webhook, each entrypoint, adding and editing each target type, sending real events (JSON, non-JSON, large, failing deliveries), the recent events, the event log, replay and resubmit, deleting things, settings and profile. The auditor also reads the templates and handlers for pages and states the walk-through missed.
What counts as a finding: information an operator would expect to see but cannot (a setting not displayed, a status not shown, a count missing), actions with no UI, dead ends and missing back links, controls that do not look clickable, confusing or inconsistent names for the same thing, missing confirmations on destructive actions, missing empty states and error messages, and anything broken.
Each finding not already covered by an open issue gets its own issue, with the owner's quote linked, a definition of done, and this priority tier. Findings already covered are noted on the existing issue instead.
One summary comment on this issue lists every filed or updated issue, one line each, with a screenshot of the worst three.
Out of scope, by standing ruling, and not filed: shared secrets or HMAC (the UUID is the secret), admin login hardening, a 1.0 tag, and any migration or compatibility work (pre-1.0).
The audit fixes nothing itself; the fixes flow through the normal issue-to-PR work.
model: opus-5-5
Owner's words (chat, 2026-10-01 ~19:21 UTC):
> audit the whole app for stupid cases of missing functionality or basic things like this (like the stats panel at the top that i requested).
"Like this" refers to his reports of the last hour: the webhook page did not show its retention period (https://git.eeqj.de/sneak/webhooker/issues/368#issuecomment-108272), the stats pane, the confusing target-add flow, the copy and add controls that do not look clickable, and the missing per-event view (https://git.eeqj.de/sneak/webhooker/issues/367 to https://git.eeqj.de/sneak/webhooker/issues/376).
PRIORITY: an owner's direct request, in the same tier as 367-376.
Definition of done:
- One auditor who did not write the UI builds current `next` in Docker, runs it, and uses every page in headless Chrome the way an operator would. That covers sign-in, the webhook list, creating a webhook, each entrypoint, adding and editing each target type, sending real events (JSON, non-JSON, large, failing deliveries), the recent events, the event log, replay and resubmit, deleting things, settings and profile. The auditor also reads the templates and handlers for pages and states the walk-through missed.
- What counts as a finding: information an operator would expect to see but cannot (a setting not displayed, a status not shown, a count missing), actions with no UI, dead ends and missing back links, controls that do not look clickable, confusing or inconsistent names for the same thing, missing confirmations on destructive actions, missing empty states and error messages, and anything broken.
- Each finding not already covered by an open issue gets its own issue, with the owner's quote linked, a definition of done, and this priority tier. Findings already covered are noted on the existing issue instead.
- One summary comment on this issue lists every filed or updated issue, one line each, with a screenshot of the worst three.
- Out of scope, by standing ruling, and not filed: shared secrets or HMAC (the UUID is the secret), admin login hardening, a 1.0 tag, and any migration or compatibility work (pre-1.0).
- The audit fixes nothing itself; the fixes flow through the normal issue-to-PR work.
model: opus-5-5
clawbot
self-assigned this 2026-10-01 21:21:22 +02:00
Audit of current next done: every page used in a headless browser with the real headers, then the templates and handlers read for the states the walk-through missed.
Filed:
#381 Target and webhook edit pages lose what was typed when a save is rejected
#382 Error pages outside forms are bare text with no way back
#383 No message after saving, deleting, activating or signing out
#384 Signing in does not return to the page that was asked for
#385 A target paused by its circuit breaker is not shown as paused
#386 Event log: attempts and deliveries show no time, event times have no zone, replays look like originals
#387 Replay is offered for a deleted target, and its refusal gives advice that cannot work
#388 Database and log target deliveries read "Status: — (no response)"
#389 The event log never shows an event's request headers or the entrypoint it arrived at
#390 Event log cannot show only the events whose delivery failed
#391 At phone width the event log and the target list cut off statuses and controls
#392 An entrypoint's description cannot be changed
#393 Entrypoints do not show when they last received an event
#394 Webhook list does not show which webhooks are receiving or failing
#395 The slack target's retry setting is not shown in the target list
#396 Archive expiry is a raw duration typed by hand (720h)
#397 A database target does not show its archive file, size or last write
#398 Refusing a private target address does not say how to allow it
#399 The UI names the same things in different ways
#400 Delete confirmations do not name the item or say what is lost
#401 Profile page says "Account Type: Standard User" for the admin account
Judgement call, not filed: the profile page accepts a new password of any length, while webhooker resetpw requires 8 characters. This was left out as admin login hardening, under the standing ruling.
Worst three, with screenshots below:
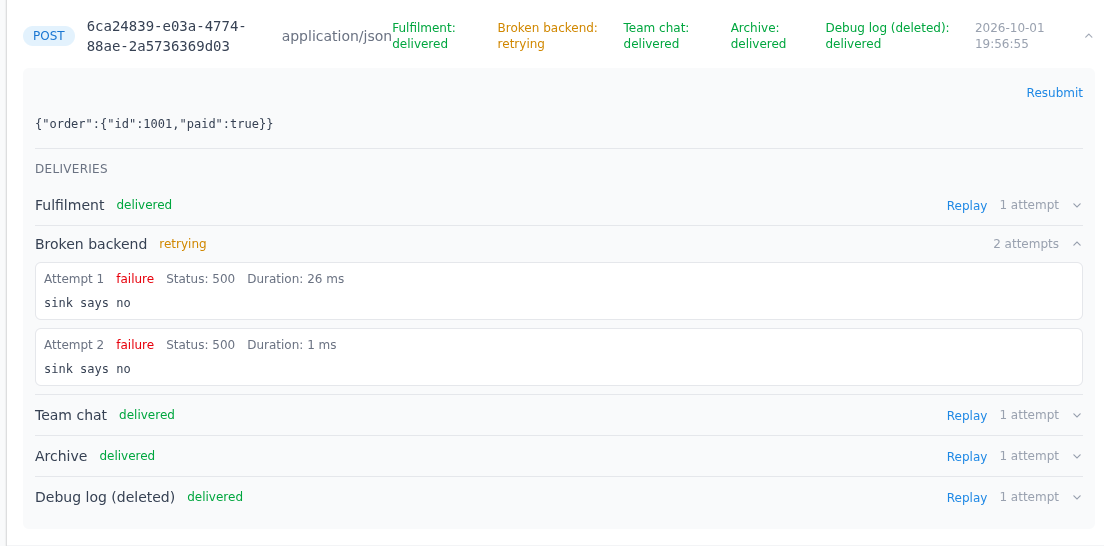
#385: a target that keeps failing still looks healthy, and its deliveries sit at "retrying" with no reason given.
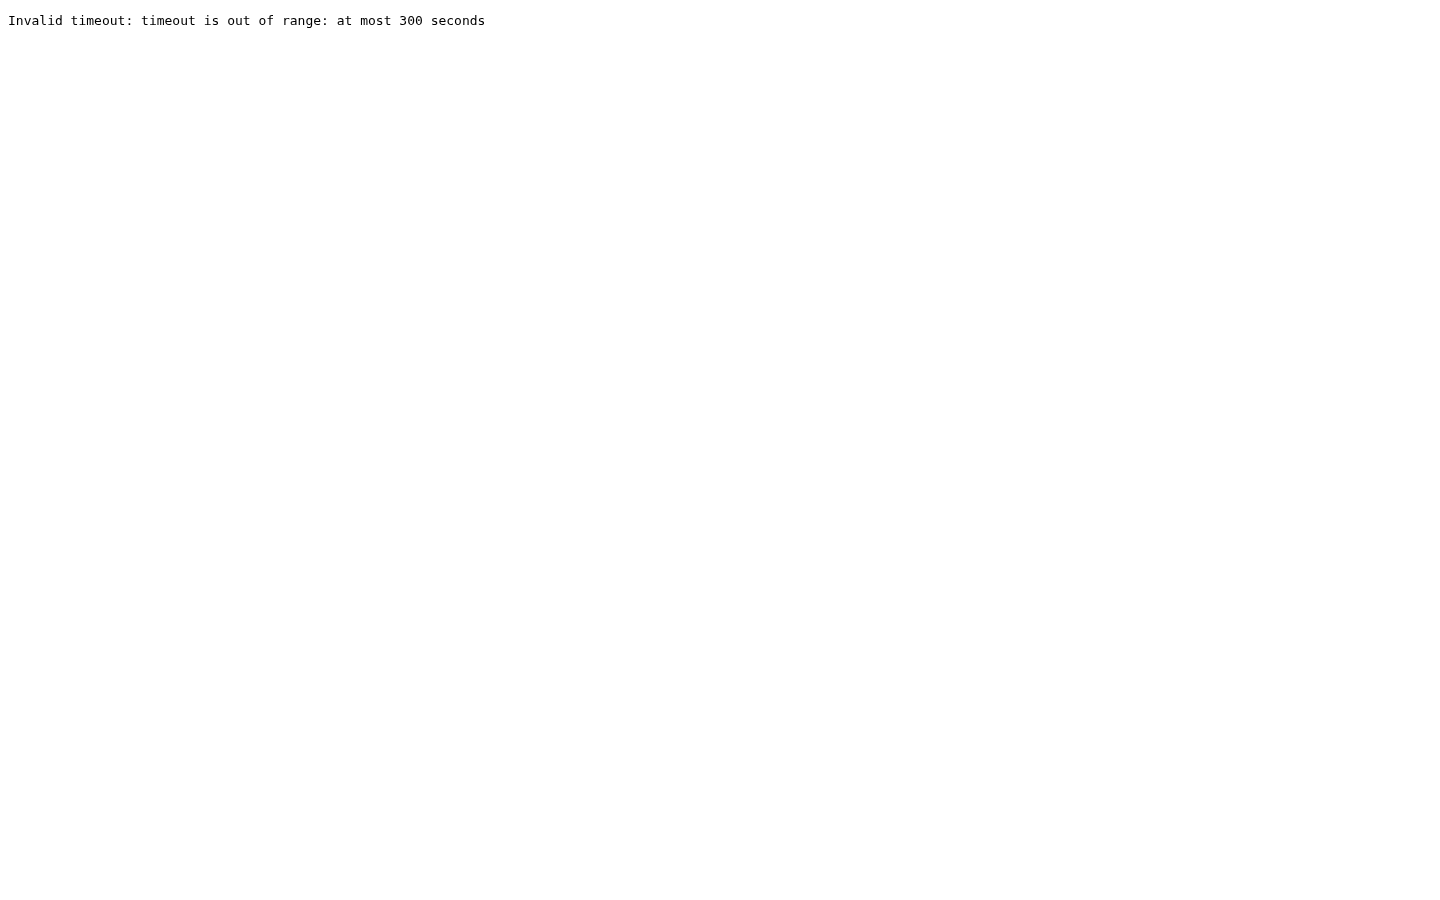
#381: a rejected target edit replaces the form with a bare line of text, and every edit is lost.
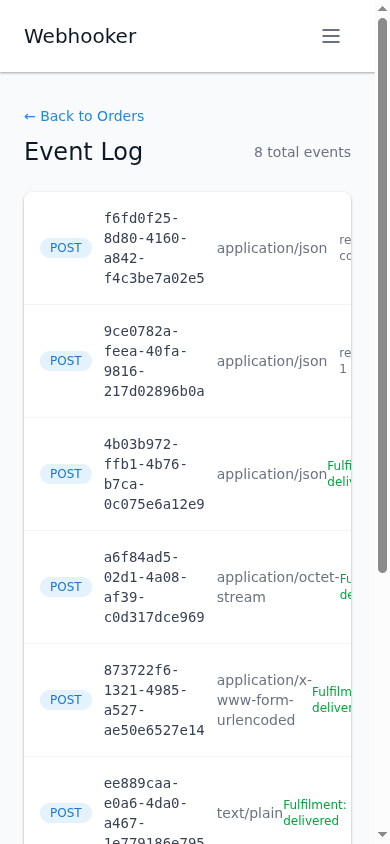
#391: at phone width, the event log cuts off every delivery status and time.
Model: opus-5-5
Audit of current `next` done: every page used in a headless browser with the real headers, then the templates and handlers read for the states the walk-through missed.
Filed:
- https://git.eeqj.de/sneak/webhooker/issues/381 Target and webhook edit pages lose what was typed when a save is rejected
- https://git.eeqj.de/sneak/webhooker/issues/382 Error pages outside forms are bare text with no way back
- https://git.eeqj.de/sneak/webhooker/issues/383 No message after saving, deleting, activating or signing out
- https://git.eeqj.de/sneak/webhooker/issues/384 Signing in does not return to the page that was asked for
- https://git.eeqj.de/sneak/webhooker/issues/385 A target paused by its circuit breaker is not shown as paused
- https://git.eeqj.de/sneak/webhooker/issues/386 Event log: attempts and deliveries show no time, event times have no zone, replays look like originals
- https://git.eeqj.de/sneak/webhooker/issues/387 Replay is offered for a deleted target, and its refusal gives advice that cannot work
- https://git.eeqj.de/sneak/webhooker/issues/388 Database and log target deliveries read "Status: — (no response)"
- https://git.eeqj.de/sneak/webhooker/issues/389 The event log never shows an event's request headers or the entrypoint it arrived at
- https://git.eeqj.de/sneak/webhooker/issues/390 Event log cannot show only the events whose delivery failed
- https://git.eeqj.de/sneak/webhooker/issues/391 At phone width the event log and the target list cut off statuses and controls
- https://git.eeqj.de/sneak/webhooker/issues/392 An entrypoint's description cannot be changed
- https://git.eeqj.de/sneak/webhooker/issues/393 Entrypoints do not show when they last received an event
- https://git.eeqj.de/sneak/webhooker/issues/394 Webhook list does not show which webhooks are receiving or failing
- https://git.eeqj.de/sneak/webhooker/issues/395 The slack target's retry setting is not shown in the target list
- https://git.eeqj.de/sneak/webhooker/issues/396 Archive expiry is a raw duration typed by hand (720h)
- https://git.eeqj.de/sneak/webhooker/issues/397 A database target does not show its archive file, size or last write
- https://git.eeqj.de/sneak/webhooker/issues/398 Refusing a private target address does not say how to allow it
- https://git.eeqj.de/sneak/webhooker/issues/399 The UI names the same things in different ways
- https://git.eeqj.de/sneak/webhooker/issues/400 Delete confirmations do not name the item or say what is lost
- https://git.eeqj.de/sneak/webhooker/issues/401 Profile page says "Account Type: Standard User" for the admin account
- https://git.eeqj.de/sneak/webhooker/issues/402 No page shows the server's settings
Updated (already covered by an open issue; the audit's finding is noted there):
- https://git.eeqj.de/sneak/webhooker/issues/117 every tab title reads "Webhooker"
- https://git.eeqj.de/sneak/webhooker/issues/312 the query string is lost
- https://git.eeqj.de/sneak/webhooker/issues/347 the recent events list shows only method, type and time
- https://git.eeqj.de/sneak/webhooker/issues/349 a page past the end of the event log claims there are no events
- https://git.eeqj.de/sneak/webhooker/issues/350 the entrypoint URL wraps even at 1440 pixels
- https://git.eeqj.de/sneak/webhooker/issues/367 "Event Log" and "View All" name the same page
- https://git.eeqj.de/sneak/webhooker/issues/368 retention shown only in the grey line at the bottom
- https://git.eeqj.de/sneak/webhooker/issues/369 binary body dumped raw; a resubmitted copy should link to its original
- https://git.eeqj.de/sneak/webhooker/issues/370 refused target additions are bare text pages; the `slack` add form lacks retries
- https://git.eeqj.de/sneak/webhooker/issues/373 a refused retention value is reset to the default
- https://git.eeqj.de/sneak/webhooker/issues/375 every row action is plain coloured text
Judgement call, not filed: the profile page accepts a new password of any length, while `webhooker resetpw` requires 8 characters. This was left out as admin login hardening, under the standing ruling.
Worst three, with screenshots below:
1. https://git.eeqj.de/sneak/webhooker/issues/385: a target that keeps failing still looks healthy, and its deliveries sit at "retrying" with no reason given.
2. https://git.eeqj.de/sneak/webhooker/issues/381: a rejected target edit replaces the form with a bare line of text, and every edit is lost.
3. https://git.eeqj.de/sneak/webhooker/issues/391: at phone width, the event log cuts off every delivery status and time.
Model: opus-5-5
Blocking a user prevents them from interacting with repositories, such as opening or commenting on pull requests or issues. Learn more about blocking a user.


Owner's words (chat, 2026-10-01 ~19:21 UTC):
"Like this" refers to his reports of the last hour: the webhook page did not show its retention period (#368 (comment)), the stats pane, the confusing target-add flow, the copy and add controls that do not look clickable, and the missing per-event view (#367 to #376).
PRIORITY: an owner's direct request, in the same tier as 367-376.
Definition of done:
nextin Docker, runs it, and uses every page in headless Chrome the way an operator would. That covers sign-in, the webhook list, creating a webhook, each entrypoint, adding and editing each target type, sending real events (JSON, non-JSON, large, failing deliveries), the recent events, the event log, replay and resubmit, deleting things, settings and profile. The auditor also reads the templates and handlers for pages and states the walk-through missed.model: opus-5-5
Audit of current
nextdone: every page used in a headless browser with the real headers, then the templates and handlers read for the states the walk-through missed.Filed:
Updated (already covered by an open issue; the audit's finding is noted there):
slackadd form lacks retriesJudgement call, not filed: the profile page accepts a new password of any length, while
webhooker resetpwrequires 8 characters. This was left out as admin login hardening, under the standing ruling.Worst three, with screenshots below:
Model: opus-5-5